Posts

About Spectre

引言 現今操作系統(OS)設計一般分為應用層 (Ring 3) 與 內核層(Ring 0) , 應用層屬於普通應用程式級別, 而內核層屬於OS的代碼, Intel CPU Spectre漏洞產生後, 有大量的非技術性文章, 但Google Project Zero的文章講得比較艱深, 因此筆者在這做一個比較簡單的解釋與定義 理論背景 Out-of-Order Execute(OoOE) -  非順序執行 即表示正常匯編語言(Assembly Language) 不按正常的順序執行, 這是因為處理器中的各個運算單元實際上是可以異步工作的, 不需要像8086等老CPU, 同步執行指令。常見的如Cache Load/Store Unit, ALU 等等 Indirect Branch Prediction (分支預測) - CPU在執行過程中, 遇上了分支的話, 會先進行分支預測, 如常見的if 則是分支指令之一, 而他對應的匯編指令一般不會等到比較后才執行, 而cpu發現比較需要更久的時間的話, 那就會把if中的內容優先執行, 而執行的內容不一定會影響到結果, 但是執行的內容使用到的緩存則不會被修改(L1/2 DCache) 詳見: The Intel Optimization Reference Manual section 2.3.2.3 ("Branch Prediction"): Spectre漏洞的產生就是基於以上兩個處理器優化機制而出現的 見以下代碼, 處理器在執行過程中, 假如arr1-length不在cache中, CPU則不會等到條件判斷完成才執行if{..}中的內容, 如果條件不成立, 才會退回對寄存器的影響, 但是arr1->data則會一直在L1 DCache中 struct array { unsigned long length; unsigned char data[]; }; struct array *arr1 = ...; unsigned long untrusted_offset_from_caller = ...; if (untrusted_offset_from_caller < arr1->length) {   unsi...
Windows Mini Class and Class Driver internal research notes

Image
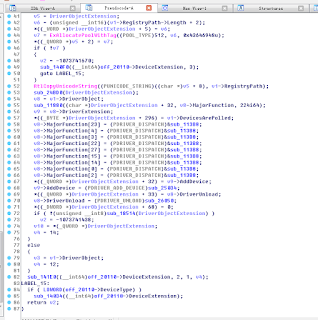
Background ------------------------------------- This is a first windows driver research notes in my blogger. And I will try to keep it simple and clear in this article, for who wants to understand the internal behavior of Class And Mini-Class Driver. ------------------------------------- Audience ------------------------------------- For who wants to understand Mini-Class and Class Driver internal. And understanding more about Hid Device stack. ------------------------------------- Introduction ------------------------------------- First, We are going to take a example of HidUsb and HidClass, the former is a Mini-Class Driver of a HidClass. We can simply think the relationships between them, is a child and parent relationship, Hidusb is one of the child of HidClass. HidClass can be thought as a helper module( like Dll do) in kernel mode, for helping all Driver who wants to join a hid family. ------------------------------------- Research ----...

Through IDA+VMWare for debugging any kernel function

Image
  Introduction : A most of time we used Windbg+ VMW are for kernel debugging. But there is a problem that we can not  use it for debug ging a  Interrupt Service Routine (ISR) . In such case system will be hang and occur a infinite loop within a interruption. Such as INT 3 breakpoint interruption. This is because the interrupt cannot be handled normally, the  breakpoint  exception is never been dispatched normally. Because of this reason, we actually can able to use a VMWare ’ debugging interfaces for debugging ISR. VMWare exported a interfaces with GDB, we can...

Nested-Virtualization - IA32_GS_BASE / IA32_KERNEL_GS_BASE remark

Image
Background:      Debugging with Nested-VMM hang issue when injecting nested #DB, and the infinite #PF occur, the system will be freeze.  Phenomenon: After Emulation of VMExit (L0 VMRESUME to L1), then causing VMExit Reason is 28 (CR access), and after that  the Kernel GS Base is changed. Try to intercept WRMSR and find the instruction which modify IA32_KERNEL_GS_BASE, therefore, as a follow screen capture: 0xFFFFF80002ADB369, which is in area of nt!SwapContext. Matched VMExit Reason PS. Because I take this screen capture at different time, so that address is not the same… and above: 0xFFFFF80002ADB369, there is a 0Xfffff80002a9c369 Analyze: -      Take a look at the red box in the following screen capture, the function will be directly execute WRMSR into a 0C0000102H (IA32_KERNEL_GS_BASE) MSR with actually qword ptr [r8+80h], r8 is an address of the current thread’s User Mode Scheduling Contro...

Intel IA-32 / Intel 64 指令架構 之 指令解碼

Image
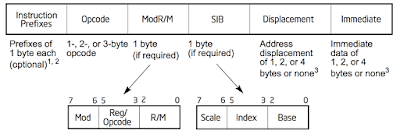
引言: ------------------------------------- IA-32 到 Intel 64 架構中 每一條匯編指令也由特定的格式給CPU的指令解碼器,或調試器的反匯編器(disassembler)解析,因而我們可以直觀地知道這些指令,第一層人類有能力看得懂的語言,其中每條指令由以下組件組成: 1. Instruction prefixes( 指令前輟) : ------------------------------------- 指令前輟分為4組: Group 1 : - Lock/repeat prefix : F0h : LOCK prefix F2h : REPNE/REPNZ F3h : REP or REPE/REPZ , F3h prefix 更預設用在POPCNT,LZCNT,ADOX指令上 - Bound prefix : Group 2: - Segment override prefix: 2Eh - CS segment override 36h - SS segment override 3Eh - DS segment override 26h - ES segment override 64h - FS segment override 65h - GS segment override - Branch hints(分支) 2Eh - 分支沒效,只有jcc指令使用 3Eh - 分支有效,只有jcc指令使用 Group 3 : 66h - Operand-size override Group 4 : 67h - address-size override LOCK prefix - 強制向cpu發送LOCK#信號,確保原子操作 Repeat prefix - 重覆執行指定指令 比如movs, cmps, scas, lods, stos, ins, outs Branch hint prefix - 用於提醒CPU,最有可能的執行路徑(分支) Operand/address-size override prefix - 用於尋址時,operand/內存的16bit / 32bit大小切換 2. Opcode...