Posts

Showing posts with the label windows kernel

Say Hello to UEFI World.
Image
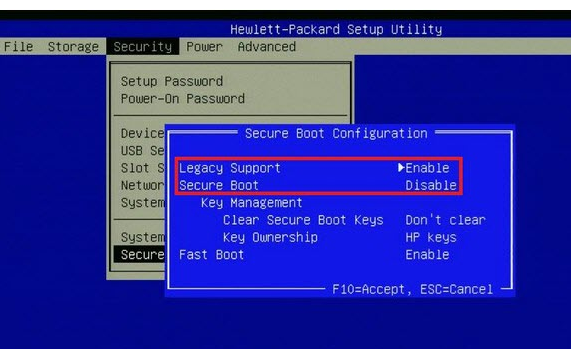
Introduction To be short... This article is going to try how could we let our EFI file get loaded under Windows 10 with disabled secure boot. Content 0. Install a VM as UEFI base VM. 1. Turn off your secure boot as following: Figure[1] 2. Mounting your GPT partition to the system by mount <drive_name> /s, so EFI partition that is visible to us. Figure[2] 3. We could place our .EFI driver / application here now (these action could be implemented programmatically, simply file coping after mounting, here is showing the concept.) 4. Configure the boot setting by SetFirmwareEnvironment API which is exported by Windows.  a) The pararmeter and GUID will be specified by UEFI spec, depend on your UEFI version.  b) For example, we need to change the BOOT#### or DRIVER#### Variable, the parameter is EFI_LOAD_OPTION as following definition: Figure[3] 5. The path of the OPTION will set as followed Figure[4] 6.  After reb...

Dig into IRQL

Image
1. Introduction ------------------------------------------------------------------------------------------------------------------- Interrupt Request Level (IRQL), is a software concept that provided by Windows, which supports an ability that management and hidden the detail of the low-level complexity of interrupt. However, as a kernel enthusiast, security researcher, it is necessaryfor understanding what it hides?? how does it worsk? This article are going to provide a simplest explanation for the IRQL. 2. Exception v.s. Trap v.s. Interrupt from processor perspectives ------------------------------------------------------------------------------------------------------------------- There are so many differences between these stuff, however, they share the only characteristic is that they also are delivered by Interrupt Descriptor Table (IDT). Exception and Trap is officially document in Intel SDM , which fixed in IDT from interrupt vector from 0 to  20 (include tr...

How does Nested-Virtualization works?

Image
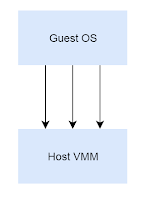
What is Nested virtualization? ----------------------------------------------------------------------------------------------------- Nowadays, Software Security is becoming more important criteria in the industry, and in recent years, virtualization as a popular topic for protecting / attacking a software, however, most of the virtualization technology framework (bluepill-liked) is not provide an ability that let a guest virtualize one more layer, we called it "Nested Virtualization", level 2. Basic Virtual Machine Monitor Architecture ------------------------------------------------------------------------------------------------------ Figure[1] Host VMM trap any type of event which wants to monitor, such as, Interrupt, exception, privileged register access, one of this event is VMX instruction, after VMM loaded, VMM can always monitor a any one of the  VMX instructions, which provide a good chance for us. As following chart: Figure[2] VMM Life Cycle ...

Windows Mini Class and Class Driver internal research notes

Image
Background ------------------------------------- This is a first windows driver research notes in my blogger. And I will try to keep it simple and clear in this article, for who wants to understand the internal behavior of Class And Mini-Class Driver. ------------------------------------- Audience ------------------------------------- For who wants to understand Mini-Class and Class Driver internal. And understanding more about Hid Device stack. ------------------------------------- Introduction ------------------------------------- First, We are going to take a example of HidUsb and HidClass, the former is a Mini-Class Driver of a HidClass. We can simply think the relationships between them, is a child and parent relationship, Hidusb is one of the child of HidClass. HidClass can be thought as a helper module( like Dll do) in kernel mode, for helping all Driver who wants to join a hid family. ------------------------------------- Research ----...